For compliance agencies
The business side of a compliance agency, in one product
Compliance automation tools watch controls. Clauseloop runs the agency around them: the pipeline and proposals, delivery with each client, the internal audit and its report, billing in the client's currency, and renewals.
For vCISO firms, managed service providers' compliance teams, and consultancies delivering ISO 27001, ISO 22301, ISO 42001, SOC 2, GDPR, HIPAA and PCI DSS programmes.
What Clauseloop does for compliance agencies
The frameworks your clients ask for
Built-in audit checklists for ISO 27001, ISO 22301, ISO 42001, SOC 2, GDPR, HIPAA and PCI DSS, next to the ISO management-system standards.
The audit stageSell and scope each engagement
A pipeline in each client's currency, proposals, and follow-up emails that go out on a schedule until the lead is won.
The win stageDeliver with the client, not over email
Clients answer the gap analysis and upload evidence in a portal in your brand, and every document carries a review status both sides can see.
The implement stageBill every engagement
Milestone invoices in 10 currencies with GST or VAT, and reminders to your team before and after each due date.
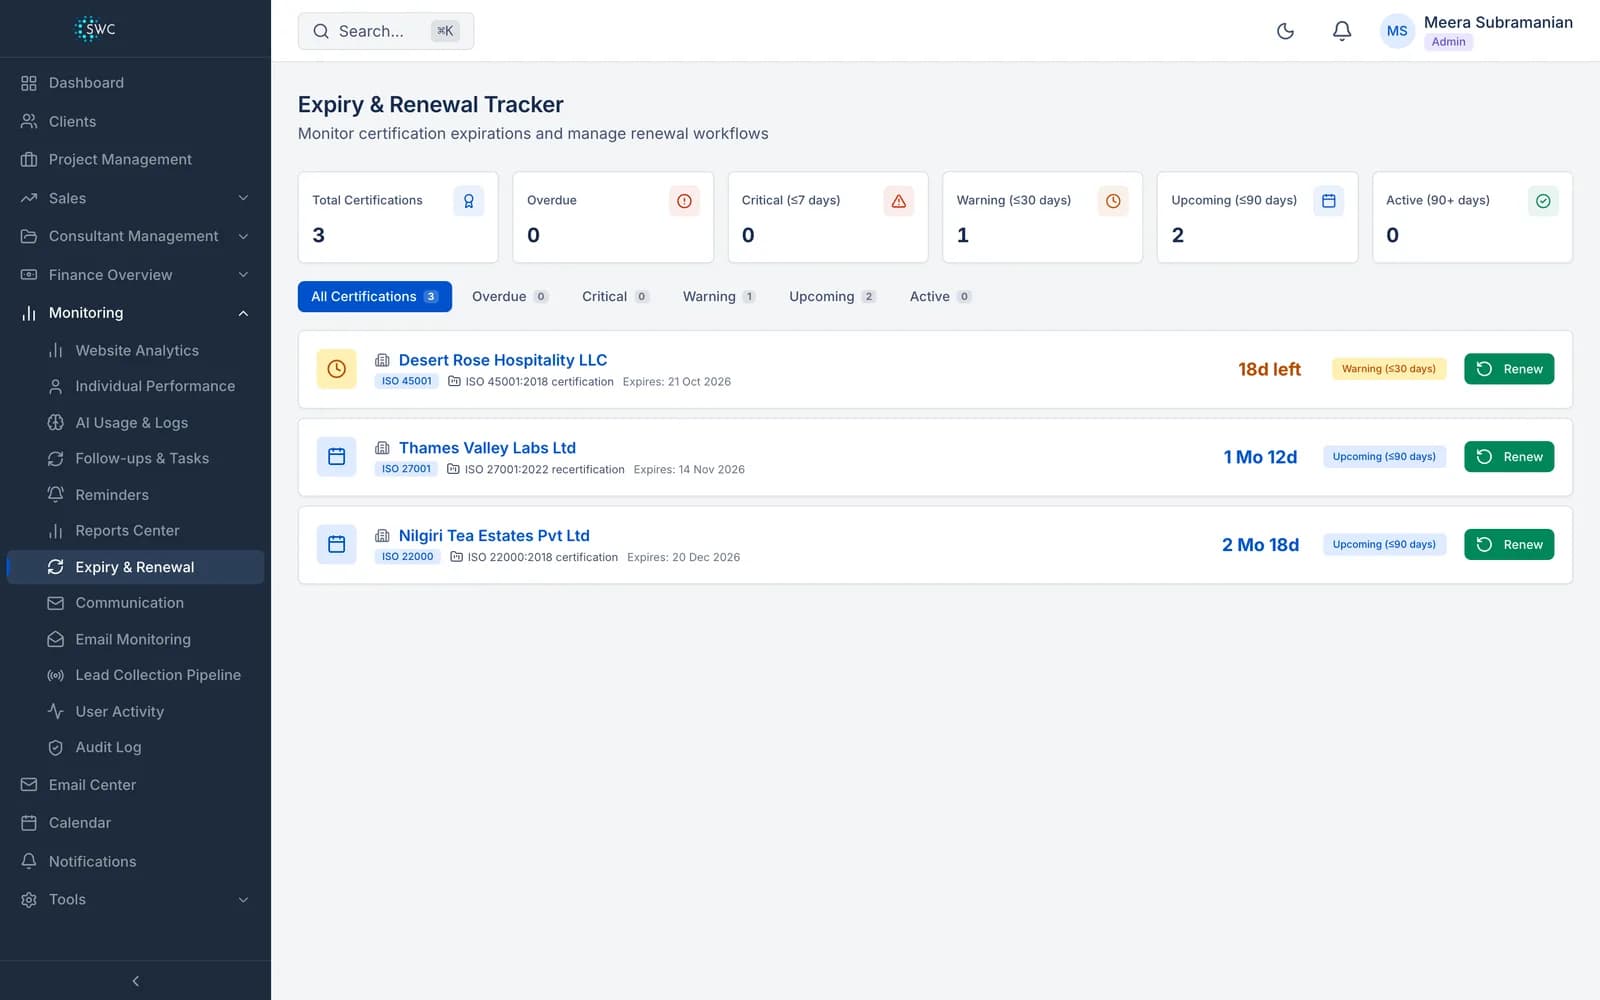
The bill stageSee every renewal before it is due
Record when each client's certificate expires. The client is emailed 90, 60, 30, 7 and 1 days before, and your team sees every expiry coming up.
The renew stageBuilt-in audit checklists
- ISO 27001
- ISO 22301
- ISO 42001
- SOC 2
- GDPR
- HIPAA
- PCI DSS
For compliance agencies: frequently asked questions
Does it monitor cloud controls like a compliance automation tool?
No. Clauseloop has no connectors to cloud accounts and does not monitor controls. It runs the agency work around that: sales, delivery with the client, the internal audit, billing and renewals.
Can I use it for SOC 2 work?
Yes, for the work an agency does: the SOC 2 checklist for internal audits and readiness, evidence from the client, billing and renewal reminders. The SOC 2 report itself is issued by an independent CPA firm.
Which security and privacy frameworks have built-in checklists?
ISO 27001, ISO 22301, ISO 42001, SOC 2, GDPR, HIPAA and PCI DSS. Other frameworks can be added for the gap analysis by uploading your own checklist as a spreadsheet template.
Also see Clauseloop for ISO consultancies.
See Clauseloop with your own clients
A 60-minute walkthrough from the first enquiry to the renewal, using the standards and currencies you work in.